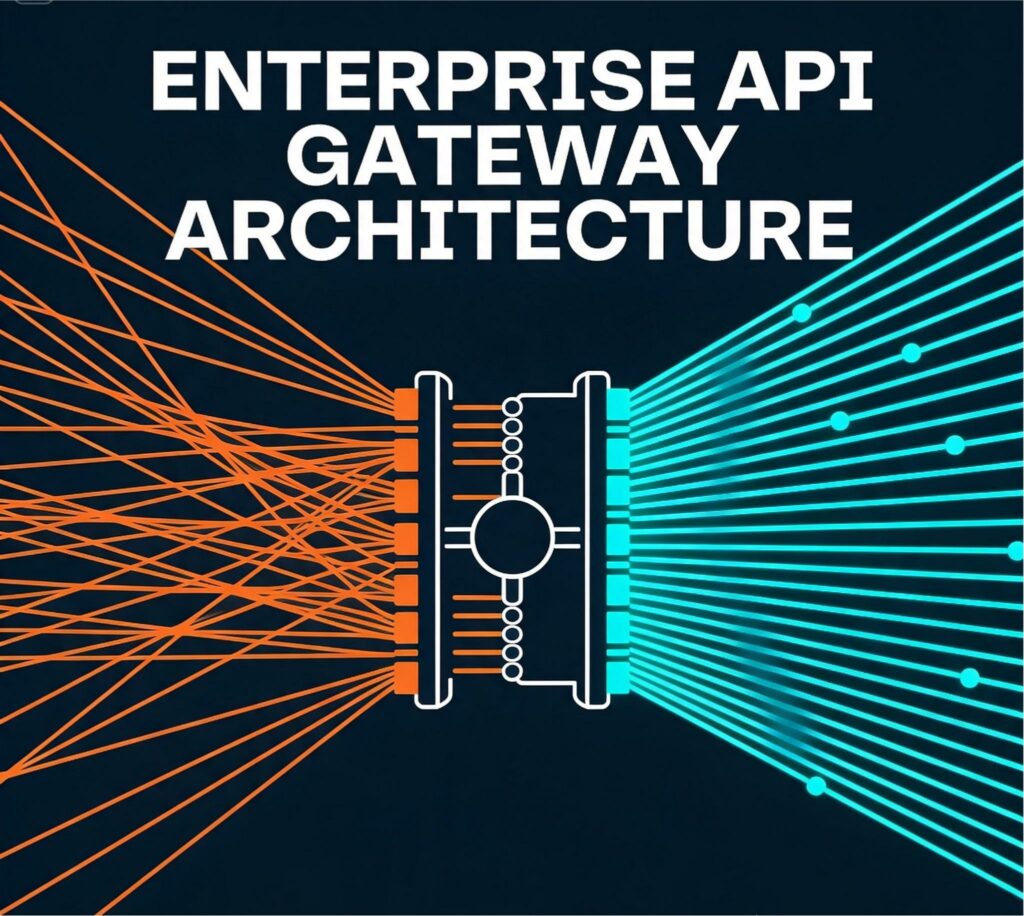
In modern microservice architectures, exposing individual microservices directly to the public internet is an architectural anti-pattern. It forces every service to independently implement authentication, CORS, rate limiting, and SSL termination.
An API Gateway acts as the single reverse-proxy entry point for all client requests, offloading edge security and traffic management from internal microservices.
1. Core Responsibilities of an Enterprise API Gateway
[Client / Mobile App] ──► [API Gateway (Edge Layer)]
                                ├─► SSL Termination
                                ├─► JWT Authentication & Scope Verification
                                ├─► Distributed Rate Limiting (Redis Sliding Window)
                                └─► Request Routing & Load Balancing
                                         │
                   ┌─────────────────────┼───────────────────── data mesh
                   ▼                     ▼                     ▼
            [User Service]       [Order Service]      [Billing Service]
- Authentication & Token Validation: The gateway validates JWT signatures and extracts user claims, forwarding sanitized headers (
X-User-Id,X-User-Role) to downstream services, eliminating redundant crypto verification in inner microservices. - Distributed Rate Limiting: Intercepts traffic spikes and DDoS attacks at the edge before backend clusters absorb the load.
- Request Routing & Path Rewriting: Dynamically proxies
/api/v1/orders/*to the Order Service cluster via internal DNS resolution.
2. Production Express / TypeScript API Gateway Middleware
Here is a streamlined core implementation of an API Gateway router handling JWT validation and Redis rate limiting:
- Note: For ultra-high-performance production environments, tools like Kong, Envoy Proxy, or Traefik are standard, but custom Node.js/Go gateways offer high extensibility for business logic.
TypeScript
import { Request, Response, NextFunction } from "express";
import jwt from "jsonwebtoken";
import Redis from "ioredis";
import { createProxyMiddleware } from "http-proxy-middleware";

const redis = new Redis(process.env.REDIS_URL!);
const JWT_SECRET = process.env.JWT_SECRET!;

// 1. Gateway Authentication Middleware
export function gatewayAuthMiddleware(req: Request, res: Response, next: NextFunction) {
  const authHeader = req.headers["authorization"];
  if (!authHeader || !authHeader.startsWith("Bearer ")) {
    return res.status(401).json({ error: "Missing or invalid authorization token" });
  }

  const token = authHeader.split(" ")[1];
  try {
    const payload = jwt.verify(token, JWT_SECRET) as any;
    // Inject sanitized headers for downstream microservices
    req.headers["x-user-id"] = payload.userId;
    req.headers["x-user-role"] = payload.role;
    next();
  } catch (err) {
    return res.status(403).json({ error: "Token expired or cryptographically invalid" });
  }
}

// 2. Gateway Rate Limiting Middleware
export async function gatewayRateLimiter(req: Request, res: Response, next: NextFunction) {
  const clientId = (req.headers["x-user-id"] as string) || req.ip;
  const key = `gateway:ratelimit:${clientId}`;

  const requests = await redis.incr(key);
  if (requests === 1) {
    await redis.expire(key, 60); // 60-second window
  }

  if (requests > 100) { // 100 requests per minute limit
    return res.status(429).json({ error: "API Rate limit exceeded. Try again later." });
  }

  next();
}